
PolicyDSL: A Model-Driven Approach for the Definition and Enforcement of Access Control Policies
We propose a unified model-driven approach for specifying and enforcing access control across the core application layers
We propose a unified model-driven approach for specifying and enforcing access control across the core application layers
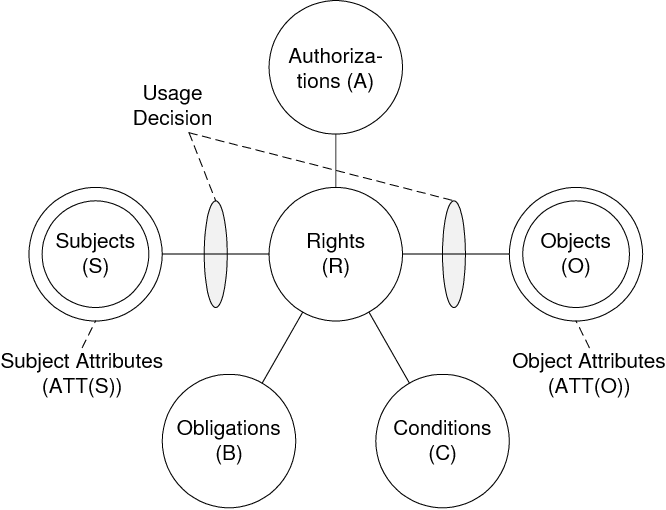
Model powerful security policies for your software designs with our DSL based on the UCON usage control model
Read about our access-control mechanisms for models. We rely on a new domain-specific language tailored to the definition of RBAC rules on models and on its enforcement thanks to the automatic generation of security compliant (virtual) views.
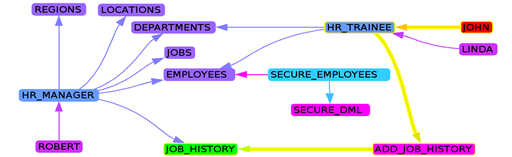
Automatic extraction of security policies that generates an RBAC security model from an existing database by analyzing its dictionary, views, triggers,…
Have you ever thought about using model transformations to specify and enforce access-control policies? Check how we do it
Recent Comments