
PolicyDSL: A Model-Driven Approach for the Definition and Enforcement of Access Control Policies
We propose a unified model-driven approach for specifying and enforcing access control across the core application layers
We propose a unified model-driven approach for specifying and enforcing access control across the core application layers
Access-control is a key element to manage security in any user interface. This is the first attempt to extend conversational user interfaces with access-control capabilities.
Read about our access-control mechanisms for models. We rely on a new domain-specific language tailored to the definition of RBAC rules on models and on its enforcement thanks to the automatic generation of security compliant (virtual) views.
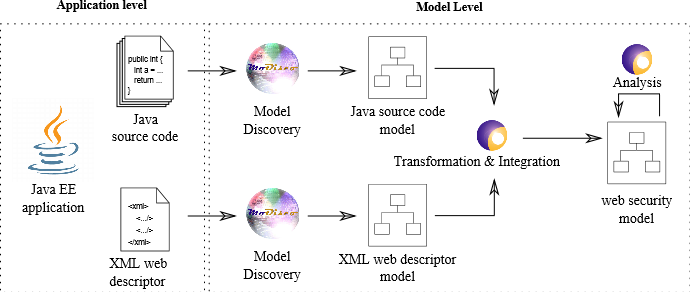
Our work helps security experts to visualize, (automatically) analyse and manipulate web security access-control policies, specially for Java EE
Have you ever thought about using model transformations to specify and enforce access-control policies? Check how we do it
Recent Comments